Optimize safely with Consize
Learn how to use consize to analyze, identify and apply safer changes with built-in guardrails without turning cost optimization into a production risk.
Stuck at any point? Troubleshooting, the FAQ, and Support are one click away from every page in the footer.
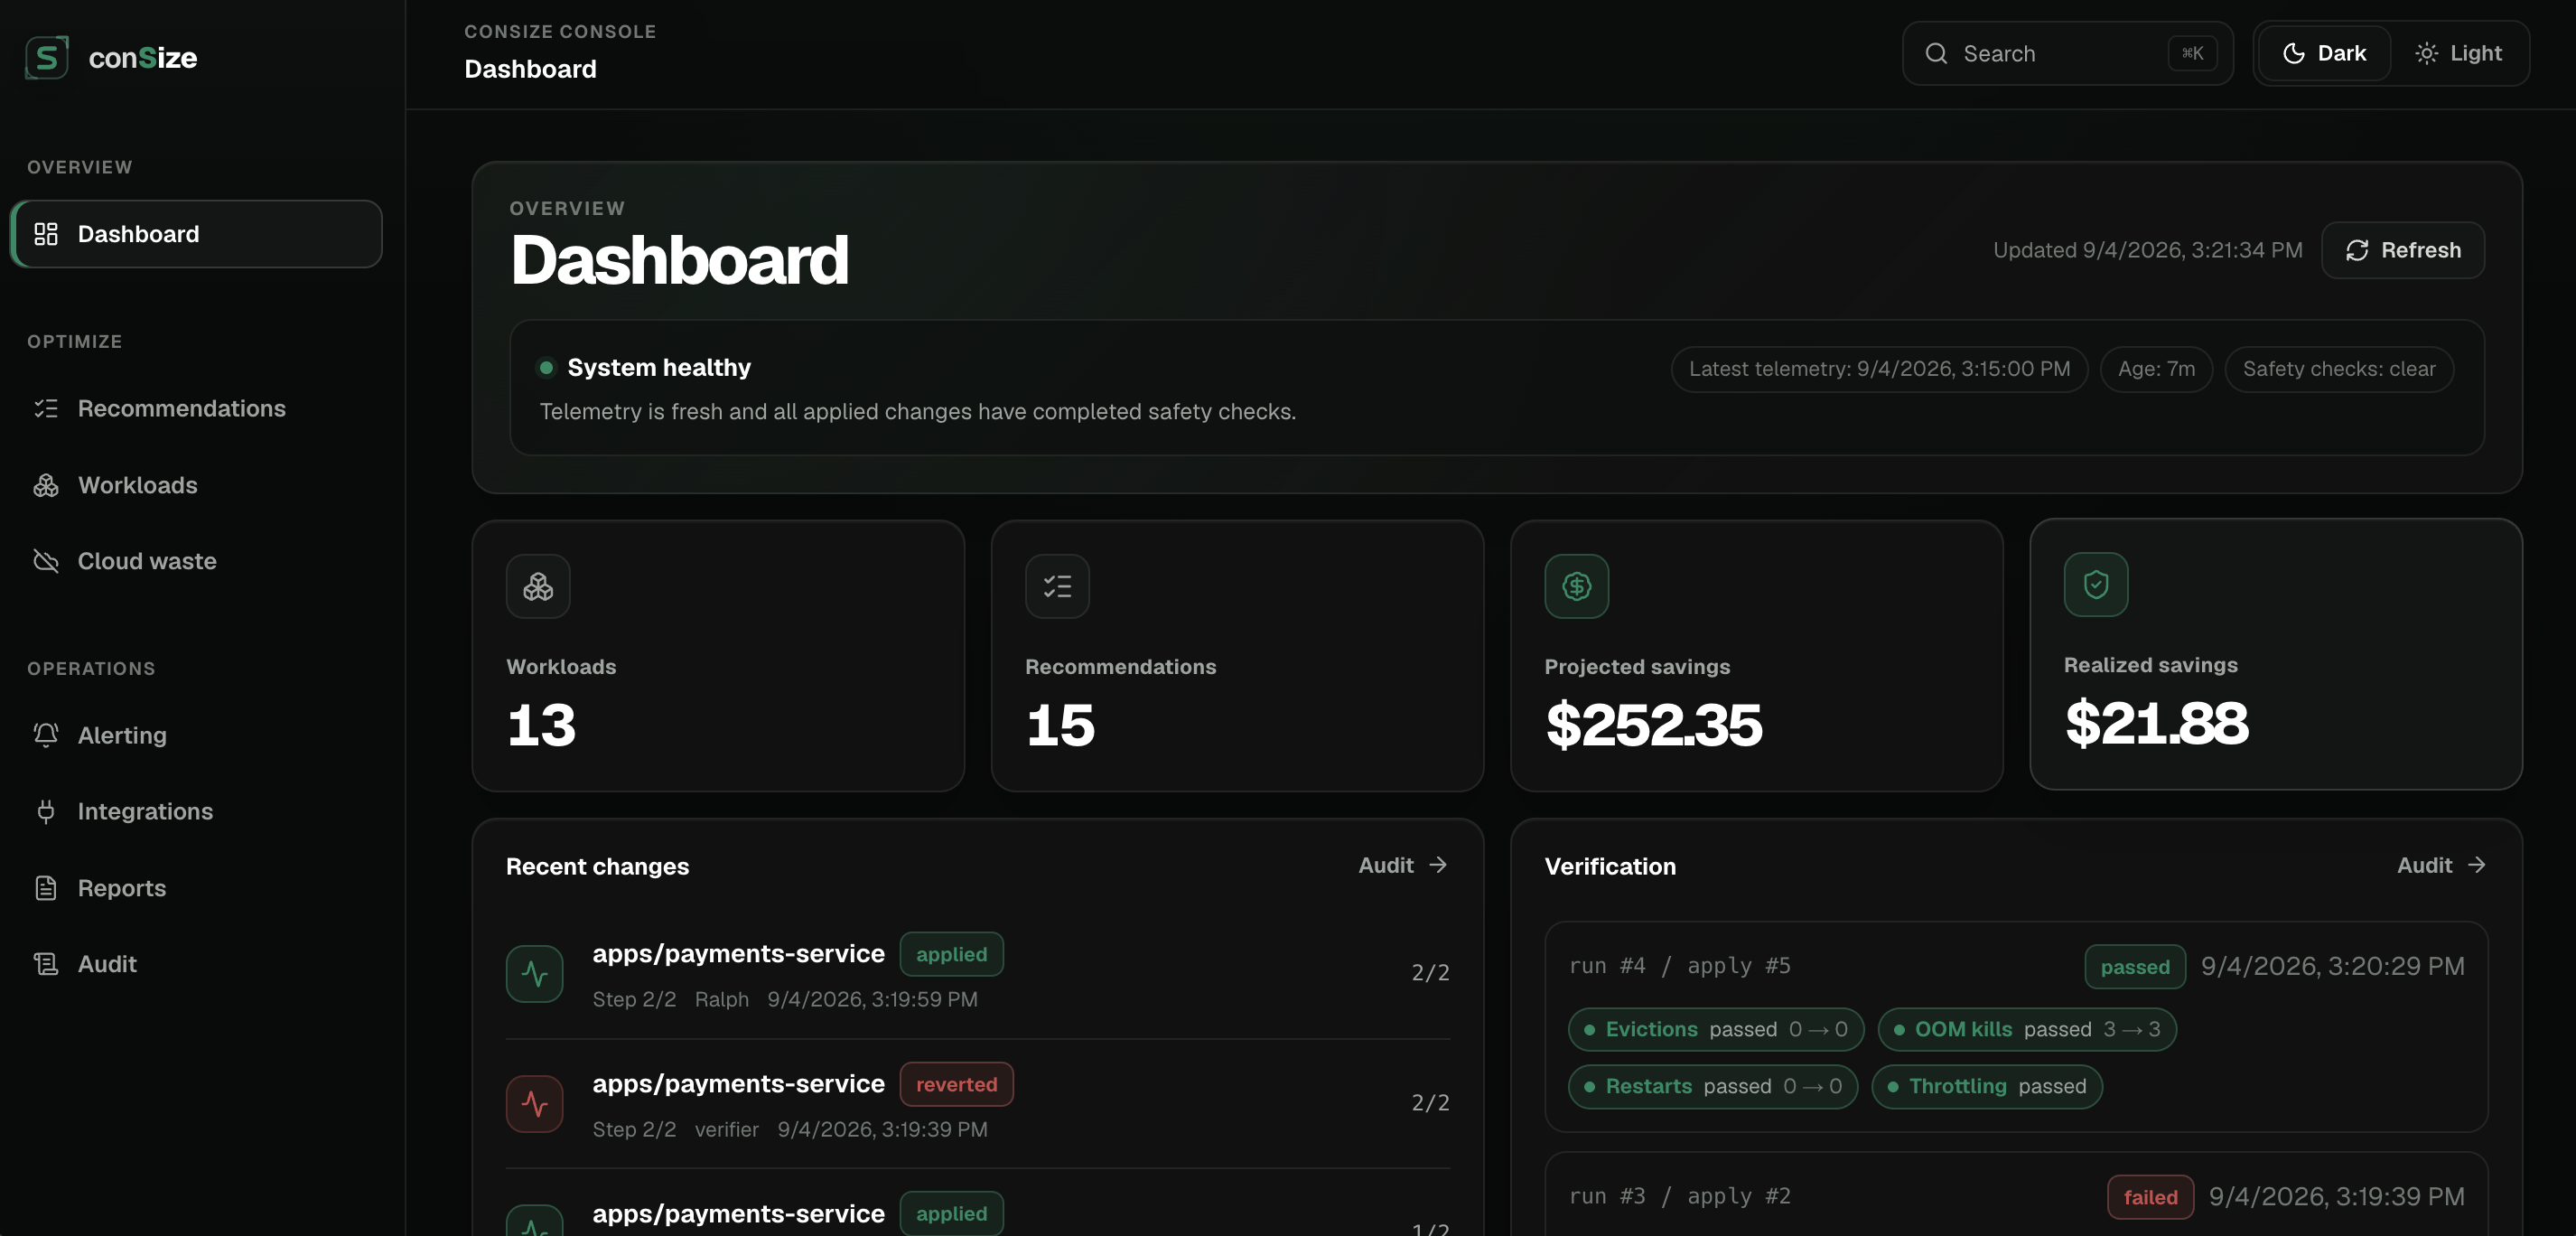
Consize continuously evaluates your infrastructure and turns resource usage data into actionable recommendations. You decide how changes are applied through reviewable pull requests against your existing Infrastructure-as-Code workflow, or as guarded runtime changes within configured boundaries.
How it works
Go from zero to a verified rightsizing change against a real workload.
1. Analyze
Point Consize at a cluster. It profiles real CPU and memory usage over a rolling window: no guesswork, no assumed sizing.
2. Review
Get a rightsizing pull request against your IaC repo, or apply approved changes directly through the UI within configured boundaries.
3. Verify
SLIs are watched after every change. If something regresses, Consize triggers an automatic, byte-identical rollback.